Configured Commerce Upgrade Watch: July 2026
sts 5.2.2607.394+sts Covers July 2026
Written by Lance Farquhar August 14, 2026
Release 5.2.2607.394+sts, published August 12, 2026. Each month we read what Optimizely says shipped, then go verify it against the actual source — frontend and backend — so you get more than a changelog recap.
The 30-Second Version
- Headline feature: ACH (eCheck) payments landed in the Payment Service via Spreedly — a full bank-account tokenization flow, not just a new button on the payment form.
- Worth knowing: Buy Now, Pay Later reached One Page Checkout too, wired into a component Optimizely had actually shipped the month before.
- One more notable item: the front-end build for Spire and Admin Console moved from npm to pnpm — a real breaking change if you maintain your own build scripts.
- Our verdict: a checkout-focused release. Two new payment methods went in cleanly on the frontend, and a quieter fix closes a real gap in how the storefront notices a session the server has already ended.
The Headline: ACH (eCheck) Payments with Spreedly
Configured Commerce's Payment Service now supports ACH — bank-account-to-bank-account transfers processed through Spreedly — alongside the existing card and other payment methods. That means a new tokenization path: bank account and routing numbers can't be handled the same way as a card number, and Spreedly's API expects its own payload shape.
The new handler, TokenizeSpreedlyBankAccount.ts, posts directly to Spreedly's payment methods endpoint with a bank-account payload and gets back a SpreedlyBankAccountTokenizationResult. On the form side, ECheckDetailsEntry.tsx picked up an iframe?: "TokenEx" | "Spreedly" union along with bank-account-type and account-holder-type selects, so the same component can render either provider's fields.
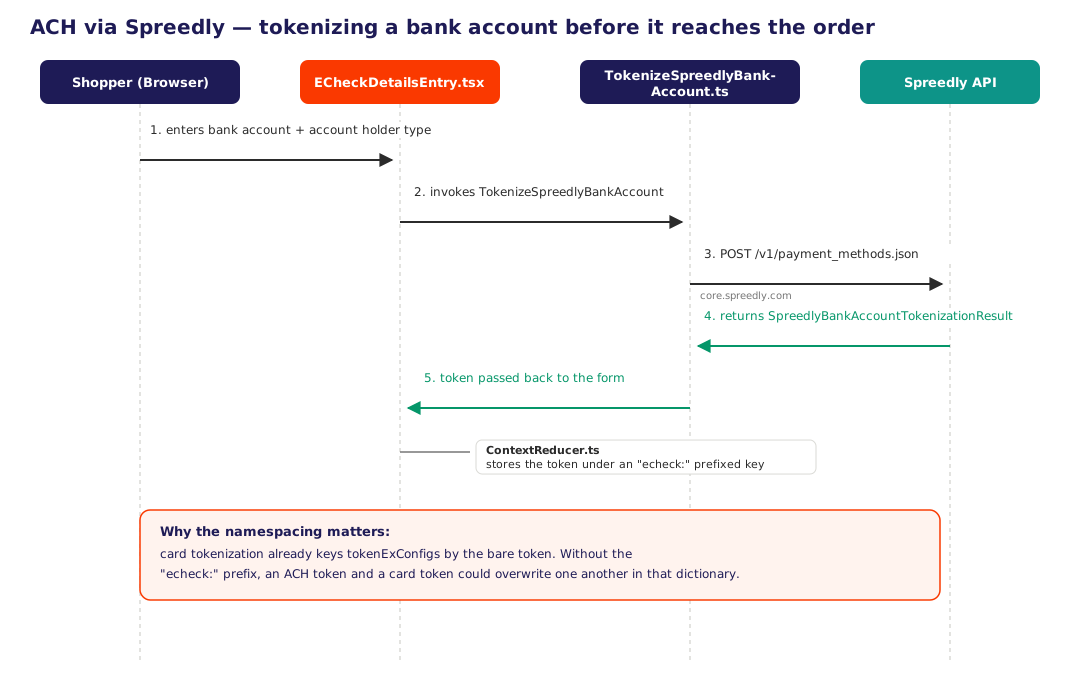
The part worth pulling out on its own is what happens once the token comes back. ContextReducer.ts now namespaces the stored TokenEx config by prefixing the key for eCheck payments:
const key = action.isECheck ? `echeck:${action.token ?? ""}` : (action.token ?? "");
draft.tokenExConfigs[key] = action.tokenExConfig;
Card tokenization already used the bare token as its key in tokenExConfigs. Without the echeck: prefix, an ACH token and a card token that happened to collide in that dictionary would silently overwrite one another. The fix is a one-line change, but it's the kind of edge case that only shows up once two tokenization flows are running through the same reducer at the same time — which is exactly the situation ACH support creates.
What Else Shipped
Breaking changes, all low risk:
- The front-end build for Spire and Admin Console moved from
npmtopnpm, for supply-chain security. This is thorough in the diff: three separatepnpm-workspace.yaml/pnpm-lock.yamlpairs were added (src/FrontEnd,src/FrontEnd/blueprintBuilder,src/InsiteCommerce.Web), all threepackage-lock.jsonfiles were deleted, and a new.npmrcand updatedvalidateLockFile.jscame with them. If you have CI scripts or local dev instructions that callnpm installornpm run, replace them with thepnpmequivalents before you build against this release. - Four new methods were added to
IDataProvider—SqlExecuteNonQuery,SqlExecuteScalar, and twoSqlExecuteStoredProcedureoverloads — andGetExternalUserIdswas added to bothIUserProfileRepositoryandIAdminUserProfileRepository. Our backend reference source doesn't have a commit for this release yet, so we weren't able to diff these against the actual interface change this cycle; if you've implemented any of these interfaces yourself, budget a direct check against your own codebase before upgrading.
Buy Now, Pay Later on One Page Checkout is real and confirmed — more on exactly what shipped below.
The Keep Me Signed In / Remember Me sign-out fixes, the Saved Payments validation fix, and the Change Customer fulfillment-method fix are all confirmed in the diff and covered in detail further down.
A long list of Admin Console and core .NET items — customer contact details in Order History, the bulk password reset action, the new Mobile Refresh Token Lifetime settings, the Application Insights SQL command text setting, request timeout middleware for the .NET 10 build, the ElasticLINQ HttpClient lifespan fix, parallelized Classic CMS theme parsing, and the Admin Console/Payment Service rebranding — all live outside the frontend repo we diff against. They're worth testing directly against a running instance rather than taking purely on the strength of the release notes this month.
A handful of listed bug fixes — the BNPL cart-ID-vs-order-number fix, the One Page Checkout confirmation-page request loop, guest order auto sign-in, CkFinder folder rename performance, and the Wishlist/VMI PDF export fix for files over 20 MB — also fall outside what we could verify this cycle, either because the relevant files weren't touched beyond formatting changes or because the underlying code lives in a repo we don't have a current commit for. Also worth testing directly if they matter to your implementation.
Eighteen bug fixes that were already shipped as 5.2.2606 hotfixes are being documented for the first time on July's release page — nothing new to check, just newly written up.
What We Actually Found: Catching a Session the Server Already Ended
Two line items in July's bug fixes read like small, unrelated cleanups: "Keep Me Signed In users not being automatically signed out after Days To Retain User elapsed," and "Remember Me mode users on .NET Framework storefronts being signed out at Site Timeout." Both trace back to the same file, SessionTimeoutWatcher.tsx, and the same underlying problem.
The session cookie is httpOnly, so client-side code has no way to see when the server has already invalidated it — the browser just keeps behaving as though the user is still signed in until something else forces the issue. SessionTimeoutWatcher.tsx closes that gap with a polling effect that checks the server every 60 seconds while keepMeSignedIn is true, backed by a visibilitychange listener so a backgrounded tab checks again the moment it regains focus, plus an expireSession() call to cover the Remember Me case. Two small endpoints carry the actual check:
GET /account/isauthenticated
DELETE /api/v1/sessions/current/authentication
The diff's own inline comment spells out the httpOnly-cookie constraint that's driving the design — worth reading if you ever need to reason about session state in a Configured Commerce storefront yourself. Two separately worded bug-fix line items, one file, one mechanism.
Under the Hood
BNPL wiring is new; the component underneath it isn't. OnePageCheckoutPaymentDetails.tsx gained a BnplPaymentSection component and four pieces of state to drive it:
// OnePageCheckoutPaymentDetails.tsx
isBnpl, bnplEnabled, bnplClientSecret, bnplTransactionToken
There's a one-second grace timer before an init-failure message shows, and the "Save & Continue" button stays disabled until both the client secret and the transaction token have arrived. BnplPaymentSection.tsx itself was actually added the month before, in June's 5.2.2606.460+sts build — July's diff is the wiring that connects it live to the checkout flow and payment-details state, not the component's first appearance.
The Saved Payments validation fix is a reordering, not new logic. SavedPaymentsEditCardModal.tsx's validate() function had its required-field checks — name, address, city, postal code — moved to run before the Paymetric-gateway readiness gate instead of after. Previously, an empty billing address could slip past validation entirely if the Paymetric iframe hadn't finished loading yet; now the required fields are checked regardless of gateway state.
The Change Customer fulfillment-method fix moves state, rather than adding a new check. ChangeCustomerSelectCustomerContainer.tsx used to bind fulfillmentMethod and pickUpWarehouse directly to session state through props. They're now local component state — renamed sessionFulfillmentMethod and sessionPickUpWarehouse, seeded from the session — that only commits back on save. Canceling the page now simply discards the local state instead of leaving the session already mutated.
What This Means for You
- If you maintain custom build scripts or CI pipelines for Spire or Admin Console, swap npm commands for the pnpm equivalents before upgrading — the lockfiles and workspace config are already pnpm-only in this release.
- If you've implemented
IDataProvider,IUserProfileRepository, orIAdminUserProfileRepositoryyourself, add the new methods (SqlExecuteNonQuery,SqlExecuteScalar, the twoSqlExecuteStoredProcedureoverloads, andGetExternalUserIds). We couldn't diff-verify the exact signatures against this release's backend source this cycle, so check your own extensions directly. - ACH via Spreedly and BNPL on One Page Checkout are both opt-in payment methods — safe to leave off until you're ready to configure and test them.
- The Saved Payments validation fix and the Change Customer fulfillment revert are both safe to take as-is; we confirmed both directly against the diff.
- Everything Admin-Console-specific — Order History contact details, bulk password reset, the new Mobile Refresh Token settings, the Application Insights toggle — is worth testing directly against a running instance rather than assuming from the release notes alone this month.
Upgrading a Configured Commerce storefront and want a second set of eyes on what actually changed under a release before you take it? That's exactly the kind of review Nishtech does for clients every month — reach out and we'll walk through it with you.